
Self-Hosted PaaS • Managed Coolify
Managed Coolify
Keep the git-push workflow, drop the 2 a.m. patching. We run Coolify for you — hardened, patched and monitored in our Frankfurt data center. Your deployments and data stay yours; the on-call becomes ours.
Open-source PaaS
Frankfurt, Germany
Patched on SLA
24/7 managed operations
No vendor lock-in
Exposed instances
Initial situation
Coolify is a great PaaS. Running it safely is a full-time job
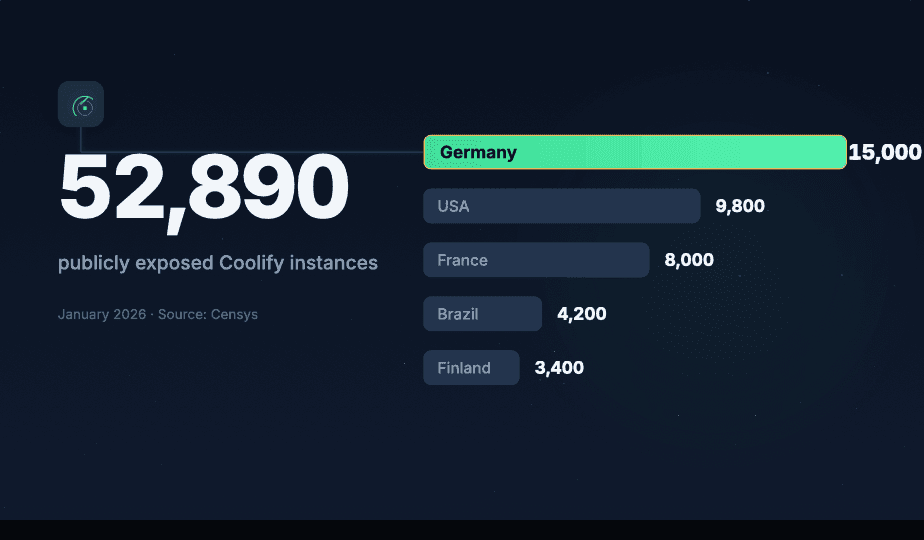
In January 2026, Coolify disclosed eleven critical CVEs in a single day — five rated CVSS 10.0, ending in root on the host. Censys counted 52,890 dashboards on the public internet, 15,000 of them in Germany. The project reacted well: fast patches, out of beta since April 2026. But new critical fixes keep landing — patching Coolify is a treadmill. The software is free; the operational duty is not.
- Dashboard VPN-only — never on the public internet
- Security patches applied on SLA — including the next CVE wave
- RBAC, secret rotation and off-host backups done properly
- Runs in Germany — your apps and data stay in the EU
The offer
What "Managed Coolify"
means at Hostzero
We run your Coolify 24/7
Security patches applied immediately
99.9% availability SLA
Dashboard never public — VPN only
No lock-in — it’s your Coolify, export anytime
Why teams move their Coolify to us
Hardened by Default
VPN-only dashboard, least-privilege RBAC, rotated secrets, off-host backups — the post-CVE hardening checklist, implemented on day one and kept current.
PaaS Workflow, Zero Ops
Keep git-push deployments, preview environments and 280+ one-click services. We handle updates, incidents and the 2 a.m. pages.
EU Data Sovereignty
Your apps and data live in our Frankfurt data center under German law — GDPR compliance you own, with a NIS2-friendly setup. Powered by renewable energy.
Self-hosted Coolify vs Managed Coolify — the honest comparison
| Criterion | Self-hosted Coolify (DIY) | Managed Coolify (Hostzero) |
|---|---|---|
Security patches | Your job — critical CVEs every few months | Applied on SLA, tested before rollout |
Dashboard exposure | 52,890 instances sit on the public internet | VPN-only, never public |
RBAC & secrets | Easy to misconfigure, keys rarely rotated | Least-privilege setup, rotation policy |
Monitoring & alerting | DIY — if at all | 24/7, included |
Backups & disaster recovery | Often on the same host | Off-host, tested regularly |
Availability | Best effort | 99.9% SLA |
Who is on call at 2 a.m. | You | Our engineers |
Cost model | Free software + your time | Fixed monthly price |
Lock-in | None | None — export and self-host anytime |
Transparent pricing
Packages & Prices
Two ways to work with us: a one-time audit & hardening of your existing instance, or fully managed operations. Fixed monthly cost — no per-seat or per-MAU fees.
Coolify Security Audit & Hardening
For existing self-hosters: we audit and lock down your instance
Managed Coolify
We run your Coolify 24/7 — hardened, patched, monitored
Migration to Managed Coolify
From DIY Coolify, Heroku, Vercel or Netlify: apps, databases and domains moved with your old setup as fallback — zero-downtime cutover.
Onboarding
From DIY to managed in days — zero downtime
Audit
Exposure, versions, RBAC and secrets of your current setup — or greenfield planning
Hardened build
A hardened Coolify runs in parallel: VPN, monitoring and backups wired in from the start
Cutover
Apps and databases move, integrity verified; your old instance stays as fallback
Operation
We run it 24/7 — patches on SLA, monitoring, backups; you keep deploying as before
Why teams choose Hostzero for Coolify
We run open-source infrastructure in production every day — Proxmox, Ceph, Keycloak, Kubernetes. Your Coolify gets the same operational discipline.
Security-First Operations
We published the post-CVE hardening guide for Coolify — and we apply every point of it to each instance we operate, starting day one.
In-House Expertise
Our own infrastructure runs on the same open-source stack. The engineers who harden your Coolify operate production systems daily.
Direct Engineer Access
No ticket queue, no middlemen — you talk directly to the people who run your stack.
In production
Client projects on Coolify — without the patching duty
Kickstage, a software development agency, runs its client projects on Coolify. After the January 2026 CVEs, "who owns patching?" stopped being a theoretical question — so the team handed us the operations: hardened setup, dashboard behind a VPN, updates on SLA. Their developers kept deploying exactly as before.
We run our client projects on Coolify, and after the January CVEs the question was suddenly: who keeps this thing patched? Hostzero took that over. The dashboard went behind a VPN, updates just happened, and we learned about the latest security release from the changelog — not from an incident. For our developers nothing changed: same git-push workflow, same dashboard.

Valentin Topolovec, Kickstage
FAQ
Frequently Asked Questions
Is Coolify safe to use in production?
After the January 2026 CVEs: yes, if it is patched fast, the dashboard is off the public internet and secrets get rotated. That is exactly what managed operations guarantee. The full analysis is in our article "Is Coolify safe?" — including a checklist if you would rather do it yourself.
Can you take over my existing Coolify instance?
Yes. We audit it, then either harden it in place or migrate it to Frankfurt — apps, databases and configuration included, with your old setup as fallback during the switch.
Do I keep the normal Coolify workflow?
Yes. Git-push deployments, the same dashboard, the same one-click services — your team keeps working exactly as before. We take over the operations underneath.
Where does my data live?
In our Frankfurt data center under German law — or on your own servers with us operating them remotely. Either way: EU data residency, no US platform in the loop.
What happens when the next CVE drops?
We patch on SLA — tested first, then rolled out. That is the core of the offer: you read about the next Coolify CVE in the news, not in your incident channel.
Can I leave?
Anytime. Coolify is Apache-2.0 open source; your data and configuration are portable. We will even help you move — no lock-in is the point of self-hosted.
Start now
Ready to stop being your own Coolify SRE?
Talk to an engineer — 30 minutes, no sales pitch. Tell us how you run Coolify today, and we will tell you honestly whether the free hardening checklist is enough — or what managed operations would change.